Understand NIST Encryption Standards for File Protection
Understanding cryptographic frameworks is critical for protecting data at rest and in transit. This guide breaks down current algorithms, regulatory requirements, and the transition to post-quantum cryptography.
The Advanced Encryption Standard (AES), specifically AES-256, remains the primary NIST-approved symmetric algorithm for securing sensitive data across finance, healthcare, and government sectors. To meet HIPAA, GDPR, and PCI DSS requirements, organizations must deploy validated full disk and file-level encryption protocols, while actively preparing for NIST’s finalized post-quantum cryptography standards (such as ML-KEM and ML-DSA) rolling out to defend against future quantum computing threats.
Reasons Encryption Standards & NIST Compliance Matter
Digital security relies on mathematical certainty. When data breaches occur, the difference between a minor incident and a catastrophic fine often comes down to one factor: was the data encrypted according to industry standards?

The National Institute of Standards and Technology (NIST) defines the cryptographic algorithms that government agencies and private enterprises trust. Compliance frameworks like HIPAA, GDPR, and PCI DSS do not mandate a selected software product; instead, they require adherence to strong cryptographic practices, primarily centered around AES (Advanced Encryption Standard) for data at rest.

Navigating the Standards
- Symmetric Encryption (AES): The backbone of file and disk security. Fast, efficient, and currently unbroken.
- Post-Quantum Cryptography: The next generation of standards designed to resist decryption by quantum computers.
- Regulatory Mapping: How technical algorithms translate into compliance for healthcare and finance.

How Modern Encryption Algorithms Work
AES-128
Uses a 128-bit key to encrypt blocks of data. It is extremely fast and offers sufficient security for standard consumer applications and low-risk data.
Best for: Mobile devices, real-time messaging, and low-latency environments.
AES-256
The gold standard for data at rest. Uses a 256-bit key, offering an unimaginably vast number of combinations. It is mandated for Top Secret government files.
Best for: Regulatory compliance (PCI DSS, HIPAA), enterprise file security, and full disk encryption.
RSA & ECC
Used primarily for data in transit and key exchange. Public keys encrypt, private keys decrypt. Elliptic Curve Cryptography (ECC) offers similar security to RSA but with smaller key sizes.
Best for: TLS/SSL certificates, secure email communication, and digital signatures.
NIST Post-Quantum Cryptography Standards
While AES-256 is highly resistant to traditional brute-force attacks, the advent of quantum computing threatens asymmetric algorithms (like RSA) via Shor's algorithm. In response, NIST has been finalizing a new suite of post-quantum cryptography (PQC) standards.

The Final Standards (2024 - 2025)
The finalized algorithms, rolling out to replace vulnerable legacy systems, include:
- ML-KEM (formerly CRYSTALS-Kyber): Designed for general encryption purposes, such as securing websites and network traffic.
- ML-DSA (formerly CRYSTALS-Dilithium): The primary standard for digital signatures.
- SLH-DSA (formerly SPHINCS+): A stateless hash-based signature scheme serving as a fallback.
NIST Selects HQC As Fifth Algorithm for Post-Quantum Encryption
As part of ongoing evaluations, NIST selected HQC as a fifth algorithm candidate for post-quantum encryption (approaching finalization in March 2025). HQC offers a various mathematical approach (code-based cryptography) compared to lattice-based schemes, offering diversity in the cryptographic toolkit in case vulnerabilities are discovered in ML-KEM.
Implement Robust Access Control withFolder Protect
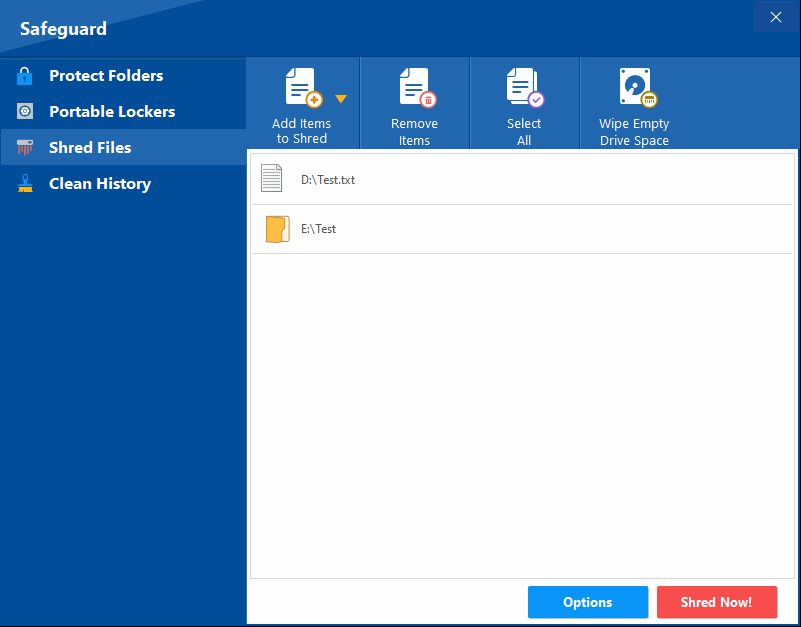
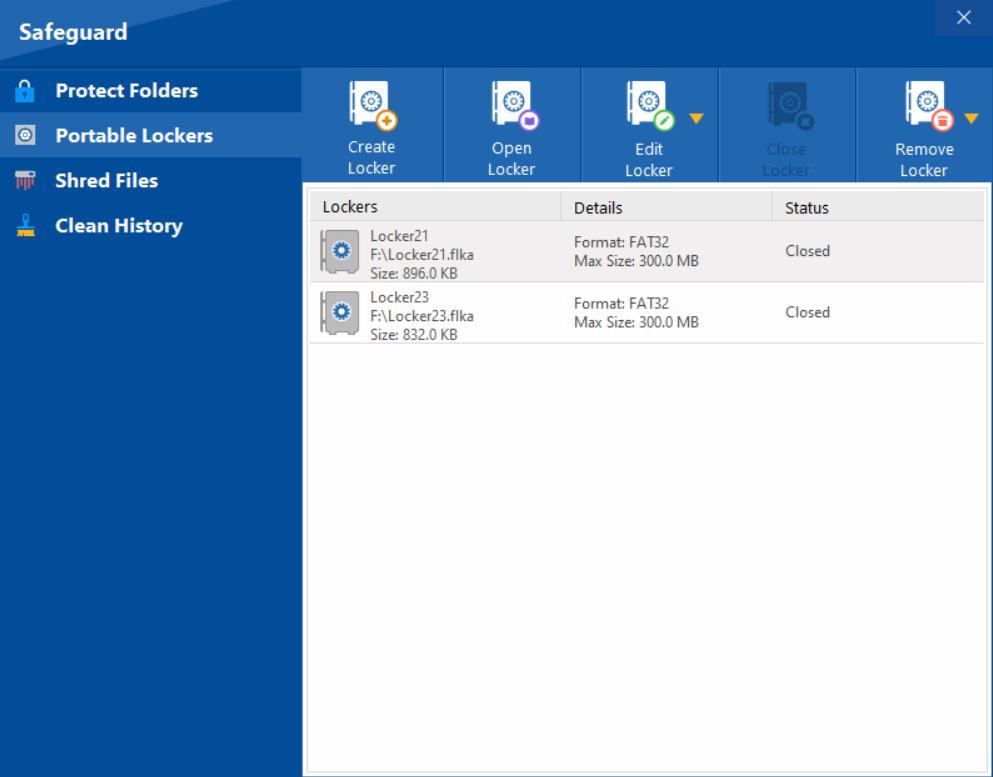
Securing sensitive local networks requires dedicated administrative tools. We recommend Folder Protect for organizations needing granular file permissions without complex command-line configurations. The application utilizes a Windows Kernel-level driver, guaranteeing that security protocols remain actively enforced even if the machine is rebooted into Safe Mode